ISO/IEC 27001 Explained in Plain Language
Understand the management system, risk decisions and evidence behind ISO/IEC 27001, with a small-company example.
Information only — not legal advice.
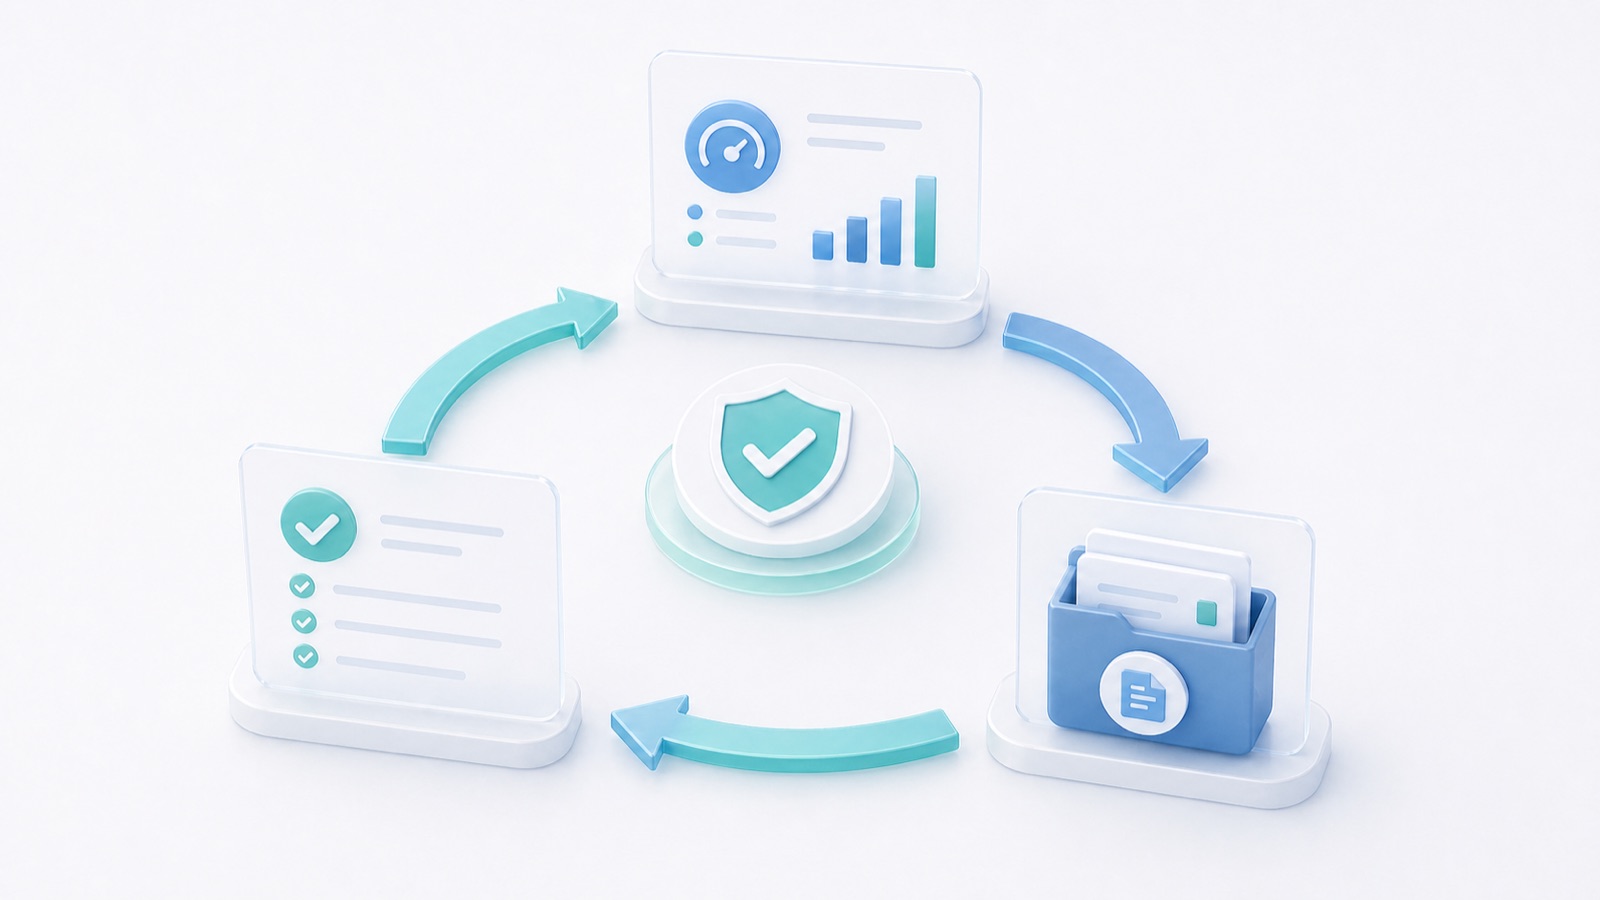
ISO/IEC 27001 sets requirements for an information security management system, or ISMS. An ISMS is the way an organization assigns responsibility, understands information risks, operates safeguards and checks whether they work. It includes people and everyday processes as well as technology.
The three familiar aims are confidentiality (appropriate access), integrity (reliable information) and availability (information available when needed). The ISO overview of ISO/IEC 27001:2022 explains the standard's purpose and the separate option of certification.
Translate the aims into everyday work
Imagine a fictional engineering practice with 25 staff:
- Confidentiality: only the payroll team should see salary details. Sending the payroll file to a general project group would defeat that restriction.
- Integrity: an issued drawing must remain identifiable. Quietly replacing it with an unchecked revision could lead to the wrong work being built.
- Availability: project information must be recoverable after a lost laptop or a failed service. A backup job marked successful is less useful than a demonstrated restore.
One incident can affect several aims. Ransomware may make information unavailable and may also expose or alter it.
Give the system a clear boundary
Define which activities, locations, people and systems the ISMS covers, and which interfaces it depends on. The engineering practice might include design delivery, project administration and supporting IT. Outsourced storage and external consultants still create dependencies to assess.
This boundary matters when evaluating a supplier's certificate: read the scope, covered services and validity, rather than relying on a logo. A certificate for one activity does not automatically cover every service a group sells. ISO itself does not certify organizations.
Work through one risk
Scenario: a former contractor can still download confidential project files.
- Describe the risk: access remains after the assignment ends, potentially exposing client information.
- Assign responsibility: the project manager owns the business risk; an administrator performs account changes.
- Choose treatment: record assignment end dates, require a departure notice and remove access through a tracked process.
- Keep evidence: retain the request and completion record, and test whether old links still work.
- Evaluate the remainder: consider downloaded copies and any continuing contractual obligations. Record who accepts the remaining risk.
- Revisit it: examine a sample of departures at the next review and fix gaps.
This is an illustrative working method, not a prescribed scoring system. Choose an assessment method people can apply consistently. The NCSC risk-management framework offers further guidance on managing and reviewing cyber risk.
Understand controls and the Statement of Applicability
A control is a safeguard: for example, access approval, staff training, a recovery procedure or supplier assurance. Select controls to address assessed risks and relevant obligations. The Statement of Applicability records the necessary controls, inclusion reasons, implementation status and justified exclusions from the reference set. It should explain the organization's decisions.
ISO/IEC 27002 provides guidance on information security controls. It complements the management-system requirements; it is not a substitute for identifying the organization's own risks. A purchased policy pack does not demonstrate that controls operate.
What evidence is useful?
In the fictional practice, useful evidence could include an access review with corrections completed, a restore exercise with observed results, a supplier assessment, training follow-up and a documented response to an incident. Each record should show what happened, who was responsible and what remained to do.
Internal audits examine whether arrangements are followed. Management reviews consider whether the system remains suitable and effective. Corrective action addresses why a failure happened and checks whether the remedy worked. Keep this work proportionate and connected to actual operations.
Certification and limitations
Certification is an independent assessment of a defined ISMS scope. It does not promise that incidents cannot happen, certify every individual file, or automatically establish GDPR compliance. Organizations can improve their security using these ideas without claiming certification.
This is an introductory explanation, not the standard's full requirements or a certification checklist. Formal work should use the applicable edition and amendments and competent advice for the intended scope.
Related reading: GDPR and Collaboration Platforms and Meeting Minutes and Action Registers.
Important information
This article provides general information and does not constitute legal advice or replace a qualified professional's assessment of your circumstances. Laws, official guidance, standards and product features can change. Check current primary sources and the requirements applicable to your jurisdiction, contract and project before making decisions. Examples illustrate the discussion; they are not official rulings or instructions for a particular case. For legal decisions, consult a qualified lawyer; for technical or other specialist matters, consult the responsible professional.
Enable JavaScript to use reading progress and usefulness ratings.